Attackers Exploit Critical Langflow RCE CVE-2026-0768 to Harvest AI Cloud Credentials
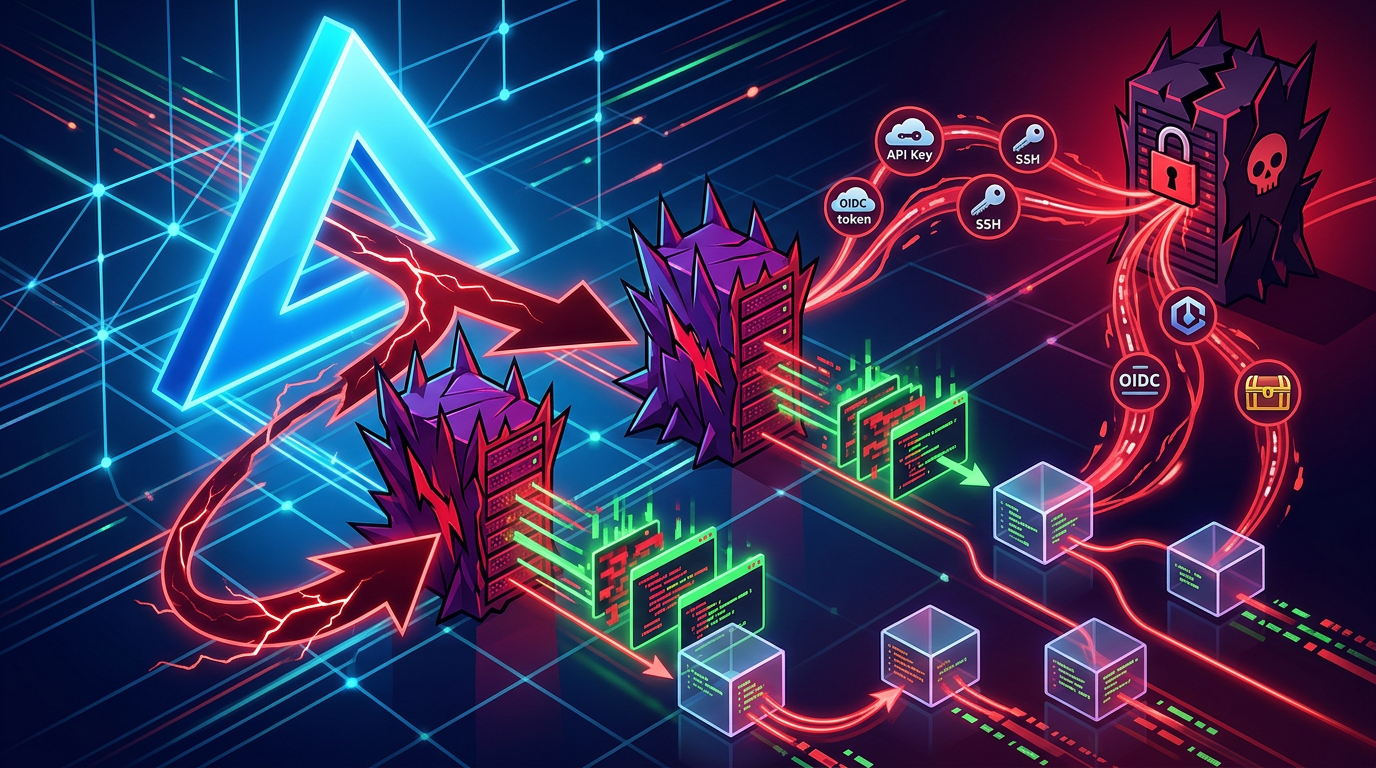
VulnCheck reports active exploitation of Langflow CVE-2026-0768 (CVSS 9.8), an unauthenticated root RCE in the custom component editor used for recon and harvesting OpenAI, AWS, and Langflow secrets.