Category Archive

Cyber Security Desk

Security-focused reporting on model operations, incident response, prompt risks, access drift, and governance.

40 stories

Coder Cloudflare Compromise Delivers Backdoored Terraform Modules to Developers

Coder Cloudflare Compromise Delivers Backdoored Terraform Modules to Developers

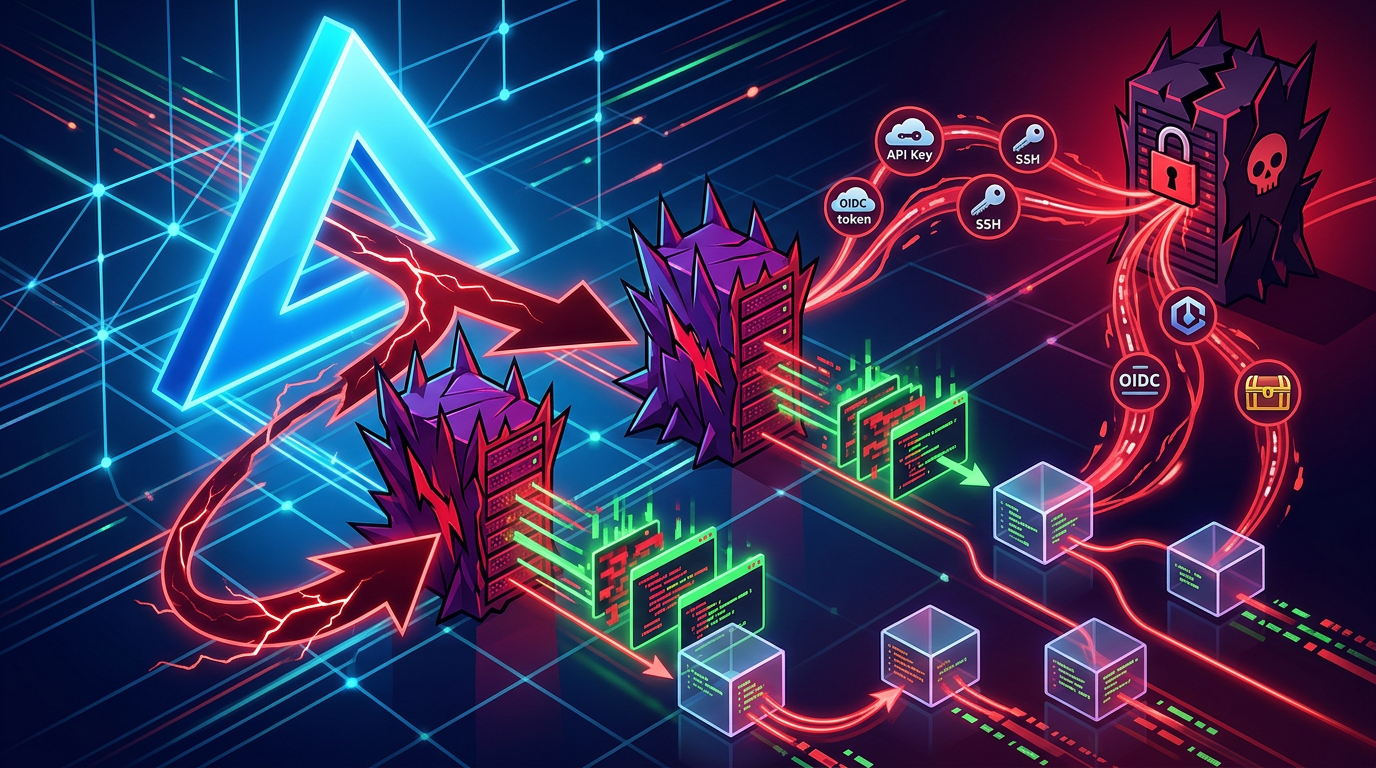
Cloud development platform Coder confirmed an attacker breached its Cloudflare infrastructure to deploy rogue registry servers that served backdoored Terraform modules. The compromised modules contained info-stealing payloads designed to harvest cloud API keys, SSH keys, OIDC tokens, and CI/CD pipeline secrets before exfiltrating them to an external server. Coder released security updates across versions 2.37.0, 2.36.4, 2.35.7, and 2.34.9, urging developers who downloaded modules during the 14-hour incident window on August 31 to rotate all credentials.

3 min read
Cisco and CISA Warn of Active Zero-Day Attacks Targeting Secure Firewall Management Center

Cisco and CISA Warn of Active Zero-Day Attacks Targeting Secure Firewall Management Center

Cisco and CISA warned that threat actors are actively exploiting a static credentials vulnerability in Cisco Secure Firewall Management Center. The flaw, designated CVE-2026-20316, stems from hardcoded low-privileged credentials in the web interface that allow remote attackers to authenticate without valid user accounts. Cisco released emergency hotfixes across FMC versions 7.0 through 10.0, and CISA ordered US federal agencies to apply patches by August 1, 2026.

3 min read
Department of War Suspends CMMC Phase II Requirements

Department of War Suspends CMMC Phase II Requirements

The U.S. Department of Defense and the Small Business Administration announced a temporary pause on Phase II of the Cybersecurity Maturity Model Certification program. The program requires defense contractors to undergo third-party assessments to verify compliance with the 110 cybersecurity requirements outlined in NIST SP 800-171 Rev 2. During the pause, the Pentagon will rely on contractor self-assessments to enforce baseline cybersecurity standards while focusing on tangible cyber hygiene over administrative overhead.

4 min read
Critical Security Flaw Patched in Joomla Helix3 Template Framework

Critical Security Flaw Patched in Joomla Helix3 Template Framework

Security researchers disclosed a high-severity improper access control vulnerability, tracked as CVE-2026-49049, in the Helix3 template framework extension for Joomla. The flaw allows unauthenticated remote attackers to delete arbitrary files, write arbitrary JSON files, and modify template parameters on exposed websites. The vulnerability affects Helix3 versions 1.0 through 3.1.1, and no official vendor patch is currently available from developer JoomShaper.

3 min read
Microsoft Defender CVE-2026-33825 Exploited in Active Ransomware Campaigns

Microsoft Defender CVE-2026-33825 Exploited in Active Ransomware Campaigns

CISA has updated its Known Exploited Vulnerabilities catalog to confirm that ransomware groups are actively exploiting a high-severity privilege escalation flaw in Microsoft Defender. The vulnerability, dubbed BlueHammer and tracked as CVE-2026-33825, allows local attackers to bypass access controls and elevate their privileges to SYSTEM level. The flaw was patched by Microsoft on April 14, 2026, but was leaked as a zero-day earlier that month by a disgruntled researcher.

4 min read
Security Flaws in Agentic AI Browsers Expose Users to Cyber Risks, University of Washington Study Finds

Security Flaws in Agentic AI Browsers Expose Users to Cyber Risks, University of Washington Study Finds

Researchers at the University of Washington evaluated seven popular agentic AI browsers and discovered that four of them expose users to significant cyber risks. The study demonstrated that ChatGPT Atlas, Chrome with Gemini, Claude for Chrome, and Perplexity Comet allow malicious sites to bypass the browser's fundamental same-origin policy. The team successfully executed a proof-of-concept prompt injection attack where a malicious webpage forced an AI agent to exfiltrate sensitive data from an embedded site.

4 min read